Workflow automation compliance means embedding your regulatory obligations directly into the systems that run your business, so approvals, access reviews, and incident escalations generate audit evidence automatically instead of after the fact. The biggest payoff is continuous, defensible proof of control, not just faster processing. GRC teams, security engineers, and operations leaders all benefit, because the same automated trail that satisfies SOC 2 auditors also cuts the manual scramble every framework renewal used to require.
TL;DR:
- Automating compliance workflows reduces manual effort by producing audit evidence automatically from activities like access reviews, policy attestations, and incident responses.
- Evidence generated by these workflows must be immutable, tagged with control identifiers, and follow best practices such as role-based access control and change logging.
- Implementing automation should start with mapping regulatory controls across frameworks, designing approval logic upfront, and pilot testing within limited system boundaries.
- Existing systems like identity providers, HRMS, and GRC platforms must be integrated with proper security measures, including encryption, RBAC, and regular vulnerability assessments.
- Key performance indicators include reducing missing evidence to below 5 percent and achieving a 30 percent reduction in engineering hours dedicated to audit preparation within 90 days.
Table of Contents
- What Compliance Workflow Automation Actually Is
- Key Benefits and Business Impact of Automated Compliance
- The Core Workflows That Generate Audit Evidence
- A Step-by-Step Implementation Roadmap
- Best Practices for Auditable-by-Design Automation
- Integration Checklist for Connectors and Verifiability
- Measuring ROI: KPIs and a 30/60/90 Plan
- Common Pitfalls in Compliance Automation Rollouts
- Regulatory Frameworks That Shape Compliance Automation
- Security Considerations and Risk Management
- The Current Platform Landscape for Compliance Automation
- Golden Path Digital’s Perspective: Map First, Automate Second
- How Golden Path Digital Supports Audit-Ready Automation
- Sources
- FAQ
What Compliance Workflow Automation Actually Is
Compliance workflow automation is not the same as general robotic process automation (RPA) or productivity tooling that just moves tasks off someone’s desk. The distinction matters because a workflow that merely speeds up a task is different from one built to survive an audit. Compliant automation is built with evidence-by-design: every step writes to an immutable, timestamped log, every action ties to a specific role under role-based access control (RBAC), and every output maps back to a named control identifier an auditor can trace. Process Street frames this as enforcing policy inside the workflow itself, not bolting a compliance check onto the end of it.
A few examples make the difference concrete:
- An access-review workflow that logs who approved a permission change and when, without anyone opening a spreadsheet.
- A policy-acknowledgment workflow that captures a timestamped attestation from every employee, versioned to the exact policy text they signed.
- An incident workflow that fires a notification and starts a countdown clock the moment a breach is detected, rather than relying on someone remembering to escalate.
Key Benefits and Business Impact of Automated Compliance
The clearest business case for compliance automation shows up in reduced audit friction and engineering hours reclaimed from manual evidence chasing.
A 2026 industry survey found that a notable portion of organizations using compliance automation reported significant reductions in audit findings and engineering manual effort, according to Scrut’s 2026 benefits report. Those numbers reflect what happens when evidence generation stops depending on a person remembering to screenshot a settings page before an auditor asks for it.
Beyond the audit itself, the ripple effects show up across the business:
- Faster customer security questionnaires and vendor reviews, because evidence is already indexed by control rather than scattered across email threads.
- Shorter investor and acquisition due-diligence cycles, since compliance posture is demonstrable on demand.
- Easier scaling across multiple frameworks (SOC 2, ISO 27001, HIPAA, GDPR) once controls are automated once and mapped to several standards.
- Lower reliance on outside consultants for routine evidence collection, since the workflow produces it as a byproduct of normal operations.
The pattern holds regardless of company size: automation pays off fastest wherever manual, recurring effort was highest to begin with, which is exactly the baseline compliance teams should measure before rolling anything out.
The Core Workflows That Generate Audit Evidence
Auditors do not want a narrative about your controls. They want artifacts, and the strongest automated workflows produce those artifacts as a natural output of doing the work, not as a separate reporting exercise.
- Access reviews. An automated access-review workflow pulls current permissions from your identity provider, routes them to the resource owner for a decision, and logs the approval or revocation with a timestamp and reviewer identity. Auditors accept this because the record shows the review actually happened on a schedule, not on a prayer that someone remembered.
- Policy lifecycle management. Distributed approval routes a new or revised policy through legal, security, and department heads, then triggers an attestation campaign tied to the exact version employees acknowledged. Version history proves which policy was live on any given date.
- Incident notification. A detected incident automatically starts a 72-hour escalation clock, common under breach-notification rules, routing alerts to legal and security leads with a logged timeline of who was notified and when.
- Continuous control monitoring. Configuration drift in a cloud environment triggers an automatic remediation ticket, and the closure of that ticket becomes the evidence artifact tied to the relevant control identifier, so the audit trail writes itself as the fix happens.
Pro Tip: Tag every piece of evidence a workflow generates with the specific control identifier it satisfies (a SOC 2 CC number or an ISO Annex A clause) at the point the workflow runs. Retrofitting that mapping months later is far slower than building it in from the start.
A Step-by-Step Implementation Roadmap
Rolling out compliance automation across an enterprise works best as a deliberate sequence rather than a single big-bang deployment. Skipping steps here is where most programs create new risk instead of removing it.
- Inventory your obligations first. List every framework you answer to, then map where controls overlap. A single access-review workflow can often satisfy evidence requirements for SOC 2, ISO 27001, and HIPAA simultaneously if you design the mapping up front, an approach Diligent recommends specifically to avoid duplicated maintenance work later.
- Design the approval and exception logic before touching tooling. Whiteboard exactly who approves what, in what order, and what happens when someone is unavailable. Automating a process nobody has actually validated just makes failures happen faster, and it widens your audit exposure rather than shrinking it, a caution PolicyCentral raises directly.
- Pick a pilot with clear integration boundaries. Start with one workflow, usually access reviews, and connect only the systems it truly needs: your HRMS for employee status, your identity provider for permissions, and your GRC platform for evidence storage.
- Set pilot metrics, then iterate. Track missing-evidence rate and time-to-remediation for 30 to 60 days before expanding.
- Scale governance alongside scope. As you add workflows, add a formal change-approval process for the automation itself, so nobody can edit an approval chain without a logged sign-off.
Best Practices for Auditable-by-Design Automation
The difference between automation that helps an audit and automation that becomes a liability comes down to a handful of control points, and auditors know exactly what to look for.
- Immutable, append-only logs. Once an event is recorded, it should be unchangeable, ideally with cryptographic integrity checks so tampering is detectable, a principle Tines outlines for building workflows that are auditable from day one.
- RBAC and segregation of duties. No single person should be able to both request and approve the same action inside a workflow; the system should enforce this, not rely on a policy document nobody reads.
- Version control on the workflow itself. Every edit to an approval chain, a routing rule, or an escalation threshold needs a change history with who made it and when.
- Exception handling with named owners. Every workflow needs a defined path for the case that doesn’t fit the standard rule, and that exception needs an assigned owner and a deadline, not an open-ended email thread.
- Evidence tagged by framework. Map each artifact to the specific control identifier it satisfies so an auditor can trace it without a translation meeting.
Integration Checklist for Connectors and Verifiability
A compliance workflow is only as good as the systems it talks to, and gaps between those systems are where most audit findings actually originate.
- Identity and access management (Okta or similar) to pull real-time permission data for access reviews.
- HRMS with SCIM sync so employee status changes, terminations especially, propagate into access and training workflows without manual entry.
- SIEM and EDR feeds to trigger incident workflows the moment a security event crosses a defined threshold.
- CI/CD pipelines where code deployment approvals themselves need an audit trail.
- GRC platforms as the system of record where evidence ultimately lands.
On the security side, expect AES-256 encryption at rest and in transit, immutable audit logs, regular vulnerability assessment and penetration testing (VAPT), and RBAC enforced at the API level, not just the user interface, as detailed in the network compliance requirements for California businesses. If workflows touch protected health information, confirm a signed business associate agreement (BAA) and data residency terms before connecting any system, guidance covered in more detail in Golden Path Digital’s HIPAA-compliant CRM requirements. Before going live, test that every automated output matches the source system record exactly. A workflow that logs an approval that never actually happened in the underlying system is worse than no automation at all.
Measuring ROI: KPIs and a 30/60/90 Plan
Before automating anything, capture your baseline: engineer hours spent per quarter on audit evidence collection, and the number of findings from your last audit cycle. Those two numbers justify the investment and give you something concrete to compare against later.
Once live, track a handful of leading indicators weekly rather than waiting for the next audit to find out something broke.
| Metric | What it signals | Target by day 90 |
|---|---|---|
| Missing-evidence rate | Percentage of controls without a logged artifact | Under 5% |
| Exception rate | Share of workflow instances requiring manual override | Declining trend month over month |
| Remediation time | Average time from drift detection to closed ticket | Under 5 business days |
| Engineer hours on audit prep | Direct comparison to baseline | 30% reduction |
Day 30 should show the pilot workflow running without daily intervention. Day 60 should show remediation times stabilizing. Day 90 is when you decide whether to expand scope based on the exception rate trend, not gut feeling.
Common Pitfalls in Compliance Automation Rollouts
Most failed compliance automation projects fail for the same handful of reasons, and nearly all of them are avoidable with a slower start.
- Automating a broken process. If your current access-review process already has ambiguous ownership, automating it just hides the ambiguity behind a faster interface. Fix the process on paper first.
- Mapping approval logic incorrectly. Sequential approvals treated as parallel ones (or the reverse) silently create gaps where nobody actually signed off, and this is one of the most common configuration errors PolicyCentral flags in enterprise rollouts.
- Integration drift. An HRMS sync that quietly fails for two weeks means terminated employees keep showing up as active in access reviews. Build alerting for integration failures themselves.
- Unclear ownership of workflow changes. Without a governance layer, someone can loosen an approval requirement and nobody notices until the audit.
Regulatory Frameworks That Shape Compliance Automation
Most enterprise compliance automation programs are built around a handful of recurring frameworks, and understanding which controls each one actually demands keeps you from over-building or under-building your workflows.
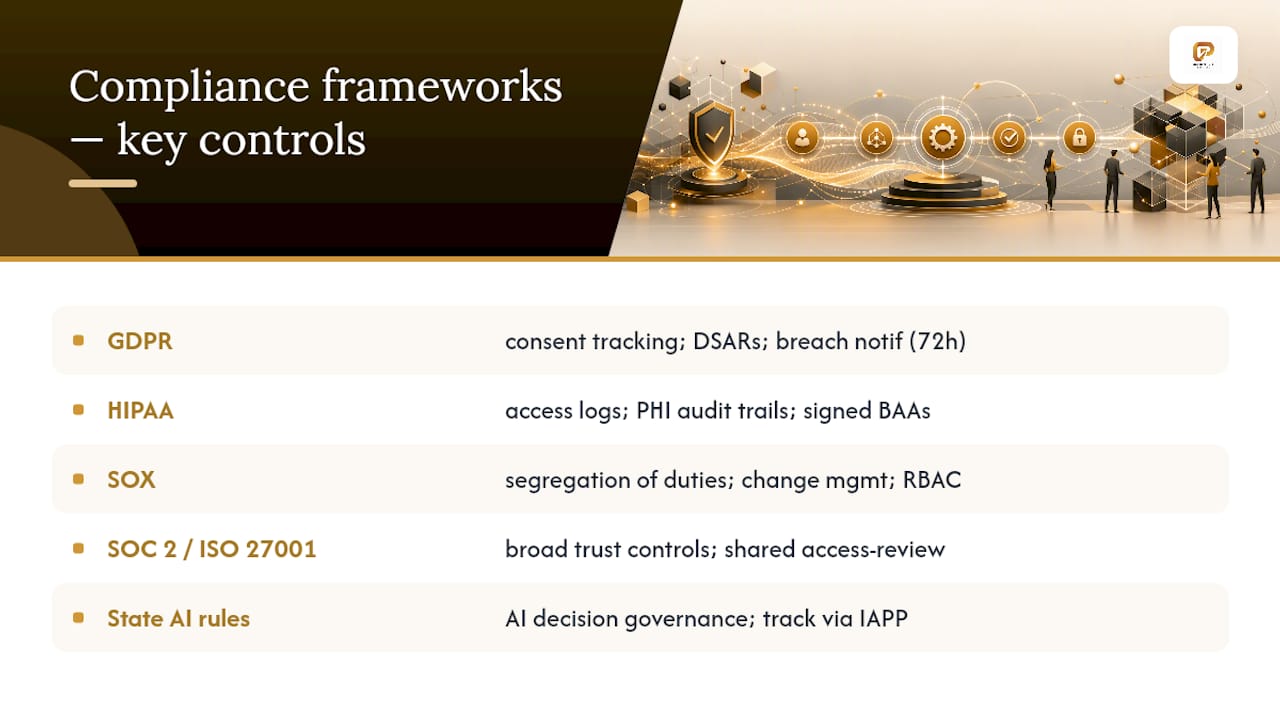
GDPR requires demonstrable consent tracking, data subject access request handling within defined timelines, and breach notification, typically within 72 hours of discovery in the EU regime many US multinationals also follow contractually. Automated data discovery and mapping make this dramatically easier to prove, a topic covered further in Golden Path Digital’s GDPR data discovery guide.
HIPAA demands access logging, audit trails on protected health information, and signed business associate agreements with every vendor touching that data. Automated audit logs here are not optional. They’re the primary evidence a regulator asks for during an investigation.
SOX focuses heavily on segregation of duties and change management around financial systems, which is precisely what RBAC-enforced workflows and version-controlled approval chains are built to demonstrate.
SOC 2 and ISO 27001 are broader trust frameworks that overlap significantly with each other and with the controls above. A single access-review workflow, correctly mapped, can often satisfy evidence requirements across all four simultaneously.
Emerging state-level AI governance rules add a newer layer. As agentic features get embedded into workflow tools, compliance teams need to track evolving requirements through resources like the IAPP’s state AI legislation tracker, since a workflow that uses AI to make a decision now carries its own governance obligations layered on top of the traditional frameworks above.
Security Considerations and Risk Management
Automating compliance workflows introduces a new category of risk alongside the risk it removes: the automation platform itself becomes a high-value target, since it now touches identity data, financial approvals, and sometimes protected health information all in one place.
Treat the automation layer with the same scrutiny you’d apply to a production system holding customer data. That means encryption at rest and in transit, strict RBAC that prevents any single account from both configuring workflows and approving the outputs of those workflows, and regular penetration testing against the platform itself, not just the systems it connects to.
Vendor risk deserves equal weight. Before connecting any third-party automation platform to your identity provider or GRC system, review its own privacy and security commitments the same way you’d review a customer contract, using something like the Microsoft privacy statement as a benchmark for the level of detail a serious vendor should publish.
AI features inside modern workflow platforms raise a distinct risk category. When a workflow uses an AI model to triage an incident or flag an anomaly, that decision needs its own audit trail, separate from the workflow’s standard logging, showing what data the model saw and what it recommended. The White House’s AI Action Plan explicitly calls out governance and auditability as prerequisites for trustworthy AI systems, and that expectation is increasingly showing up in vendor contracts and customer security questionnaires alike. If your workflow platform can’t explain an AI-driven decision after the fact, that’s a gap worth closing before an auditor finds it for you.
The Current Platform Landscape for Compliance Automation
Enterprise teams generally choose between three categories of tooling, and the right fit depends less on company size than on how many frameworks you’re juggling and how much of your infrastructure is already API-accessible.
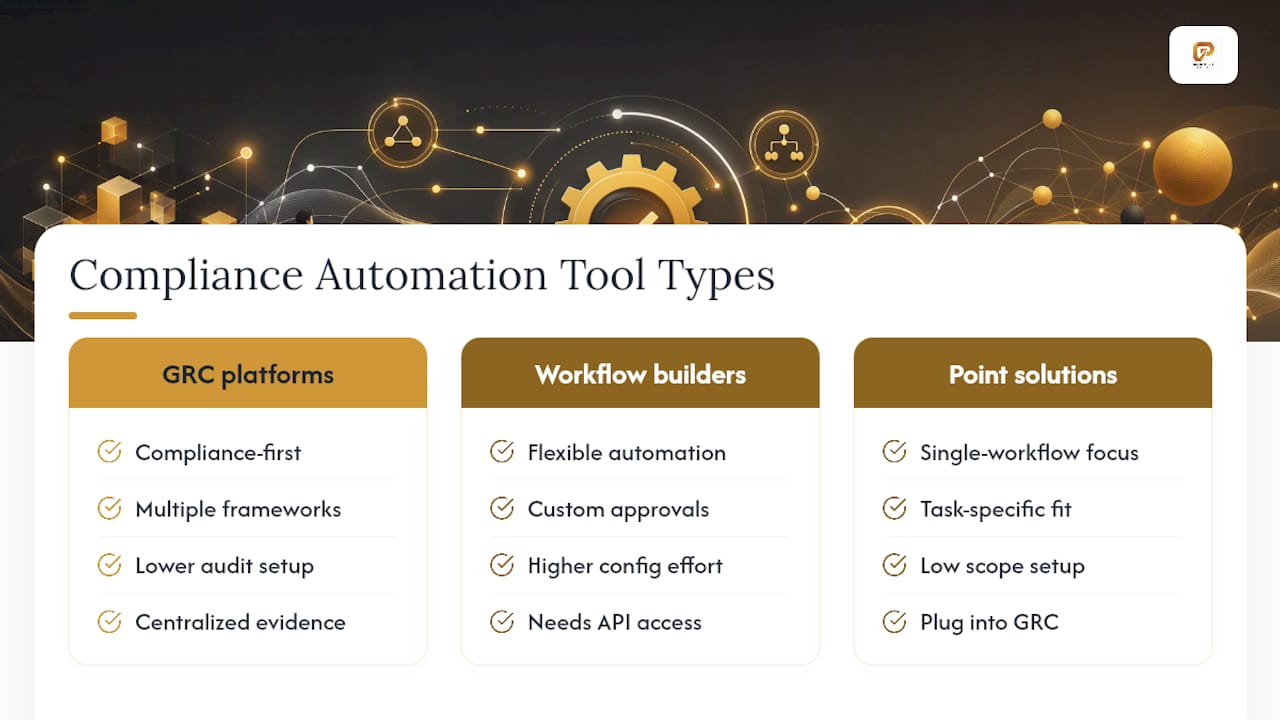
Dedicated GRC platforms center compliance as the primary function, handling evidence collection, control mapping, and audit prep in one system. These fit teams managing multiple frameworks simultaneously who need a single source of truth for auditors.
General workflow and automation builders offer more flexibility to design custom approval chains and integrations but require more upfront configuration to meet audit-grade logging standards. A review of the top workflow automation tools breaks down which tool classes fit which use cases.
Point solutions handle a single workflow type extremely well, such as access certification or policy attestation, and often integrate into a broader GRC platform rather than replacing one.
For enterprises carrying legacy systems, particularly IBM i or older Laravel applications, the harder problem usually isn’t picking a platform. It’s exposing clean, reliable data from decades-old codebases so any automation platform can actually connect to it. That’s a dependency and integration problem before it’s a tooling one.
Golden Path Digital’s Perspective: Map First, Automate Second
Most compliance automation vendors sell the workflow first and worry about your legacy integrations later. Some vendors do the opposite, starting by parsing and mapping IBM i RPG codebases or applying similar logic to framework upgrades, because building trustworthy access-review workflows requires documented dependencies.
Certain AI platforms extend that discipline into CRM and workflow automation, with privacy-standard compliance built in rather than added later. A recommended pilot sequence is to map dependencies first, run one workflow as a pilot, then integrate with a GRC platform once the pilot proves stable. Skipping the mapping step can create new audit risk instead of removing it.
Ty
How Golden Path Digital Supports Audit-Ready Automation
If your compliance program depends on legacy systems that were never built to talk to modern GRC tools, some platforms are designed specifically to address that gap. Where a general automation platform assumes clean, accessible data, Golden Path Digital starts by mapping the dependencies inside your IBM i RPG codebase or aging Laravel application, so the workflows you automate afterward actually connect to reliable, current information instead of a black box.

Some services span dependency mapping, AI for workflow and CRM automation, and HIPAA-aware integration work for teams handling protected health information. For enterprises weighing a pilot, the practical next step is an IBM i modernization assessment that maps your actual dependencies before a single workflow gets automated. If Laravel is the constraint instead, Laravel Ascend automates the framework upgrade path so your compliance workflows sit on a current, supportable codebase. Schedule a consultation to scope your pilot at Golden Path Digital.
Sources
This article draws on Scrut’s 2026 compliance automation benefits report for adoption outcomes, Tines and Process Street for auditable-by-design principles, PolicyCentral for implementation sequencing, and the White House’s AI Action Plan for AI governance context. Each addresses a distinct piece of the compliance automation puzzle, from measurable outcomes to control design to regulatory direction.
- Benefits of compliance automation: Scrut 2026 report
- Workflow Automation Compliance | Process Street
- America’s AI Action Plan (White House)
FAQ
What is workflow compliance?
Workflow compliance means a business process enforces regulatory or policy requirements as it runs, generating a timestamped, auditable record of what happened rather than requiring someone to document it afterward.
What are examples of workflow automation?
Common examples include automated access reviews, policy acknowledgment and attestation campaigns, incident notification with escalation timers, and continuous control monitoring that opens remediation tickets when configurations drift.
What are the 5 key areas of compliance?
Definitions vary by framework, but most enterprise programs organize around access control, data protection, incident response, policy management, and audit evidence retention.
What are some examples of compliance automation?
Examples include automated SOC 2 evidence collection, HIPAA access logging, GDPR data subject request routing, and vendor risk questionnaires that pull from a centralized evidence repository. Platforms like Golden Path Digital’s QuantaPath AI extend this into CRM and workflow automation with privacy-standard compliance built into the process.